Latest sovereign cloud news and innovations
Latest sovereign cloud news and innovations
- New whitepaper: Sovereign AI on your termsBuild and scale AI without compromising control across your infrastructure, data, models, and agents.
- Enterprise search on Google Distributed CloudRun managed retrieval-augmented generation search with source citations completely inside your air-gapped security perimeter.
- Google Cloud named a Leader in The Forrester Wave: Sovereign Cloud PlatformsExplore why Google Cloud was recognized as a Leader in the Q2 2026 evaluation for our AI and portfolio of choice.
Get complete control without compromising functionality
Sovereignty where you need it
Our sovereign cloud portfolio empowers governments and regulated enterprises with tailored controls across public cloud regions, partner-operated national clouds, and air-gapped on-premises environments.
Engage with independent regional operating partners
Work with trusted local partners for transparent operations, independent oversight, external key management, and regional support under local law.
Sovereign AI on your terms
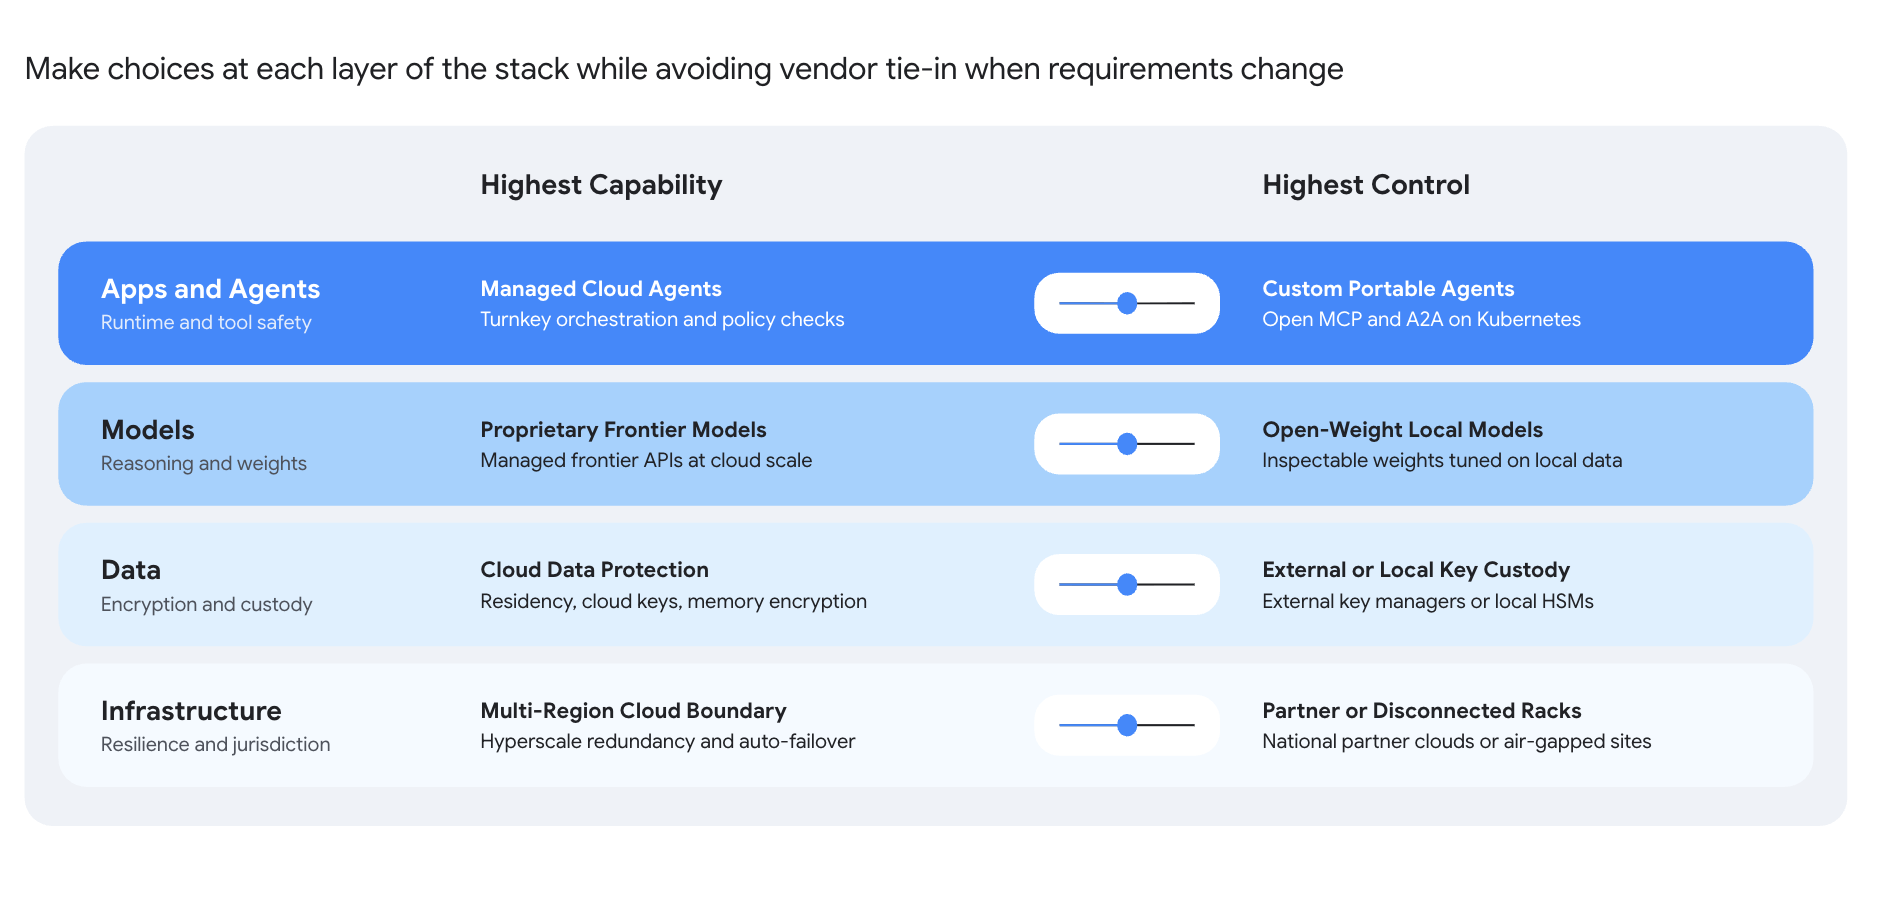
Compose a complete AI architecture across your infrastructure, data, models, and agents—combining frontier Gemini and open-weight Gemma models with built-in encryption and runtime governance.
Commitment to a secure, open digital world
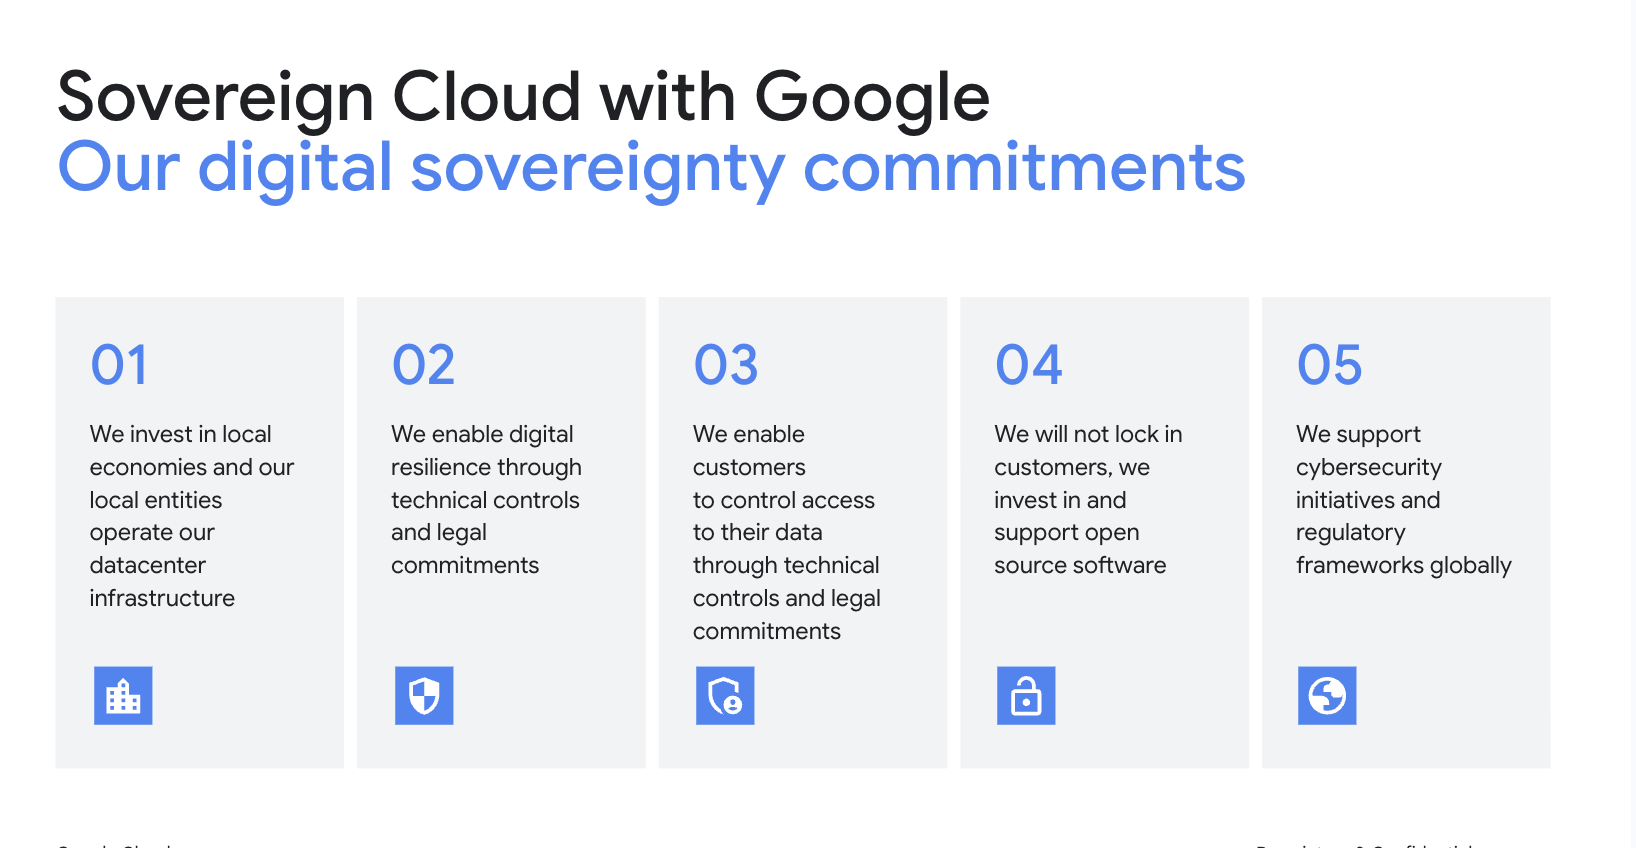
Our digital future goes beyond technology—it is about supporting a prosperous, secure, and resilient economy for the essential services citizens and businesses rely on every day.
Through our five digital sovereignty commitments, we invest in local infrastructure and skills, assure operational continuity, protect sensitive data, champion open standards without lock-in, and support evolving cybersecurity and regulatory frameworks.
Get complete control without compromising functionality
Sovereignty where you need it
Our sovereign cloud portfolio empowers governments and regulated enterprises with tailored controls across public cloud regions, partner-operated national clouds, and air-gapped on-premises environments.
Engage with independent regional operating partners
Work with trusted local partners for transparent operations, independent oversight, external key management, and regional support under local law.
Sovereign AI on your terms
Compose a complete AI architecture across your infrastructure, data, models, and agents—combining frontier Gemini and open-weight Gemma models with built-in encryption and runtime governance.
Commitment to a secure, open digital world
Our digital future goes beyond technology—it is about supporting a prosperous, secure, and resilient economy for the essential services citizens and businesses rely on every day.
Through our five digital sovereignty commitments, we invest in local infrastructure and skills, assure operational continuity, protect sensitive data, champion open standards without lock-in, and support evolving cybersecurity and regulatory frameworks.
A portfolio of choice
Run your workloads on your terms. Choose from a flexible portfolio tailored to your unique risk profile—delivering the ideal balance of local control, robust security, and regulatory compliance.
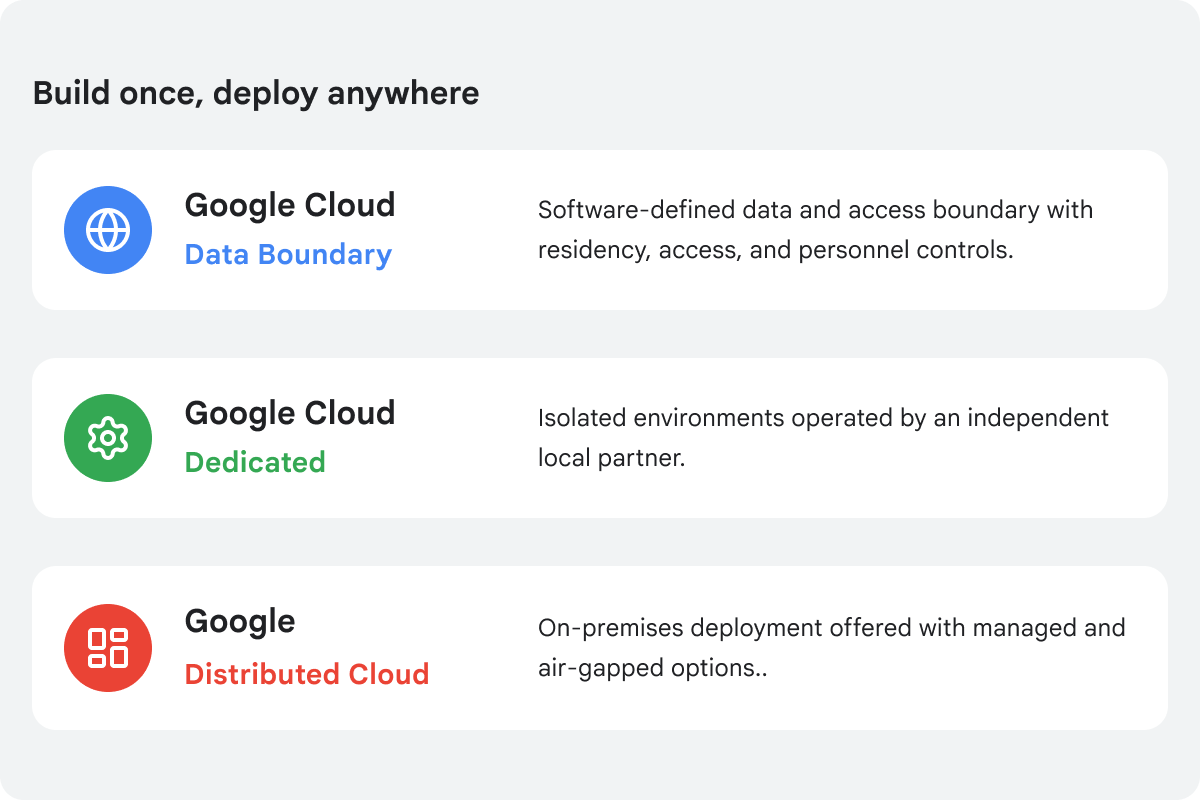
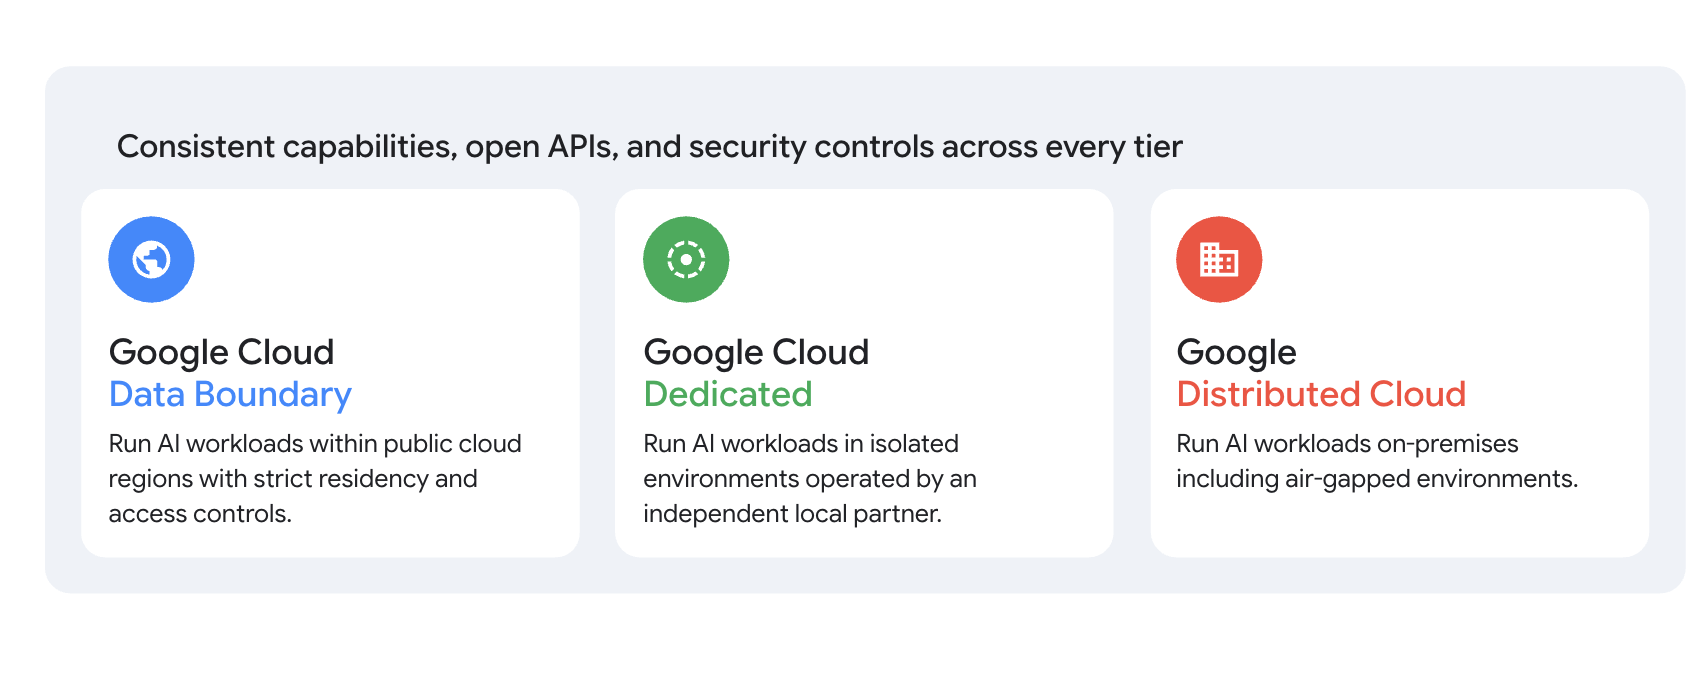
Google Cloud Data Boundary (public cloud)
Enforce software-defined policies to tailor your data residency and access controls across more than 25 regional and regulatory boundaries. Restrict support access by jurisdiction and personnel clearance, hold your encryption keys externally with Cloud External Key Manager (EKM) and Key Access Justifications, and collaborate with regional partners for independent oversight.
Sovereign AI and continuous compliance: Build with Gemini and the Gemini platform using guaranteed in-region machine learning processing, Confidential Computing, and Model Armor—while generating continuous audit evidence in Audit Manager to support mandates such as the EU AI Act, DORA, NIS2, Protected B, and FedRAMP High.
Google Cloud Dedicated (partner-operated)
Meet strict operational sovereignty requirements on dedicated, isolated infrastructure operated independently by a trusted local partner under local law—designed to continue operating for up to twelve months if disconnected from Google. In France, S3NS, a Thales company, operates PREMI3NS, which holds France's ANSSI SecNumCloud 3.2 qualification across IaaS, CaaS, and PaaS—and Google Cloud and Thales are expanding this sovereign cloud model to Germany.
AI-ready infrastructure and ecosystem compatibility: Run GPU-accelerated AI, analytics, and core enterprise workloads on Google Cloud architecture under local European operation.
Google Distributed Cloud (on-premises)
Bring Google Distributed Cloud infrastructure, security, data, and AI directly to your data centers or tactical edge on modular commercial hardware and Kubernetes. Choose connected mode for low-latency local residency, or air-gapped mode—accredited up to U.S. DoD Impact Level 6 (IL6)—for complete physical isolation from the public internet that operates independently and cannot be remotely accessed or shut down by Google.
Disconnected sovereign AI: Run Gemini, open-weight Gemma models, sovereign enterprise search (RAG) with source citations, and pre-trained AI APIs—including Cloud Translation, Speech-to-Text, and Document AI—entirely inside your local or classified perimeter.
A portfolio of choice
Run your workloads on your terms. Choose from a flexible portfolio tailored to your unique risk profile—delivering the ideal balance of local control, robust security, and regulatory compliance.
Google Cloud Data Boundary (public cloud)
Enforce software-defined policies to tailor your data residency and access controls across more than 25 regional and regulatory boundaries. Restrict support access by jurisdiction and personnel clearance, hold your encryption keys externally with Cloud External Key Manager (EKM) and Key Access Justifications, and collaborate with regional partners for independent oversight.
Sovereign AI and continuous compliance: Build with Gemini and the Gemini platform using guaranteed in-region machine learning processing, Confidential Computing, and Model Armor—while generating continuous audit evidence in Audit Manager to support mandates such as the EU AI Act, DORA, NIS2, Protected B, and FedRAMP High.
Google Cloud Dedicated (partner-operated)
Meet strict operational sovereignty requirements on dedicated, isolated infrastructure operated independently by a trusted local partner under local law—designed to continue operating for up to twelve months if disconnected from Google. In France, S3NS, a Thales company, operates PREMI3NS, which holds France's ANSSI SecNumCloud 3.2 qualification across IaaS, CaaS, and PaaS—and Google Cloud and Thales are expanding this sovereign cloud model to Germany.
AI-ready infrastructure and ecosystem compatibility: Run GPU-accelerated AI, analytics, and core enterprise workloads on Google Cloud architecture under local European operation.
Google Distributed Cloud (on-premises)
Bring Google Distributed Cloud infrastructure, security, data, and AI directly to your data centers or tactical edge on modular commercial hardware and Kubernetes. Choose connected mode for low-latency local residency, or air-gapped mode—accredited up to U.S. DoD Impact Level 6 (IL6)—for complete physical isolation from the public internet that operates independently and cannot be remotely accessed or shut down by Google.
Disconnected sovereign AI: Run Gemini, open-weight Gemma models, sovereign enterprise search (RAG) with source citations, and pre-trained AI APIs—including Cloud Translation, Speech-to-Text, and Document AI—entirely inside your local or classified perimeter.
Sovereign AI on your terms
Sovereignty now extends beyond where data is stored to how models process information and how AI agents act on your behalf. Build a complete sovereign AI architecture with modular control across infrastructure, data, models, and agents—without sacrificing innovation or risking lock-in.
A composable AI stack you control at every layer
An AI stack is only as sovereign as the layer you cannot control or replace. Google Cloud gives you modular control across every layer of your AI architecture—from who operates the underlying infrastructure and where your encryption keys live, to which models you serve and how your AI agents are governed in production.
Choice of frontier, open-weight, and regional models
Adopt the right model for every workload without vendor lock-in. Combine Google frontier Gemini models with our open-weight Gemma models—or deploy leading third-party and regional models such as Mistral through Model Garden. Fine-tune models on your own data within your sovereign boundary to reflect local languages, domain context, and regulatory standards.
Verifiable encryption and runtime AI governance
Protect sensitive prompts, training data, and model weights at rest, in transit, and in use. Enforce in-region machine learning processing, hold your own keys outside Google infrastructure with Cloud External Key Manager (EKM) and Key Access Justifications, and isolate AI workloads in memory using Confidential Computing on GPUs. Safeguard AI apps and agents at runtime with Model Armor, backed by continuous compliance evidence in Audit Manager.
Deploy AI anywhere—from public and local clouds to air-gapped environments
Built on open standards and Kubernetes, our sovereign portfolio lets your teams build AI workflows once and run them wherever your risk profile demands: in regional public clouds with Google Cloud Data Boundary, in partner-operated national clouds with Google Cloud Dedicated, or completely disconnected from the internet with Google Distributed Cloud.
Sovereign AI on your terms
Sovereignty now extends beyond where data is stored to how models process information and how AI agents act on your behalf. Build a complete sovereign AI architecture with modular control across infrastructure, data, models, and agents—without sacrificing innovation or risking lock-in.
A composable AI stack you control at every layer
An AI stack is only as sovereign as the layer you cannot control or replace. Google Cloud gives you modular control across every layer of your AI architecture—from who operates the underlying infrastructure and where your encryption keys live, to which models you serve and how your AI agents are governed in production.
Choice of frontier, open-weight, and regional models
Adopt the right model for every workload without vendor lock-in. Combine Google frontier Gemini models with our open-weight Gemma models—or deploy leading third-party and regional models such as Mistral through Model Garden. Fine-tune models on your own data within your sovereign boundary to reflect local languages, domain context, and regulatory standards.
Verifiable encryption and runtime AI governance
Protect sensitive prompts, training data, and model weights at rest, in transit, and in use. Enforce in-region machine learning processing, hold your own keys outside Google infrastructure with Cloud External Key Manager (EKM) and Key Access Justifications, and isolate AI workloads in memory using Confidential Computing on GPUs. Safeguard AI apps and agents at runtime with Model Armor, backed by continuous compliance evidence in Audit Manager.
Deploy AI anywhere—from public and local clouds to air-gapped environments
Built on open standards and Kubernetes, our sovereign portfolio lets your teams build AI workflows once and run them wherever your risk profile demands: in regional public clouds with Google Cloud Data Boundary, in partner-operated national clouds with Google Cloud Dedicated, or completely disconnected from the internet with Google Distributed Cloud.
Our digital sovereignty commitments
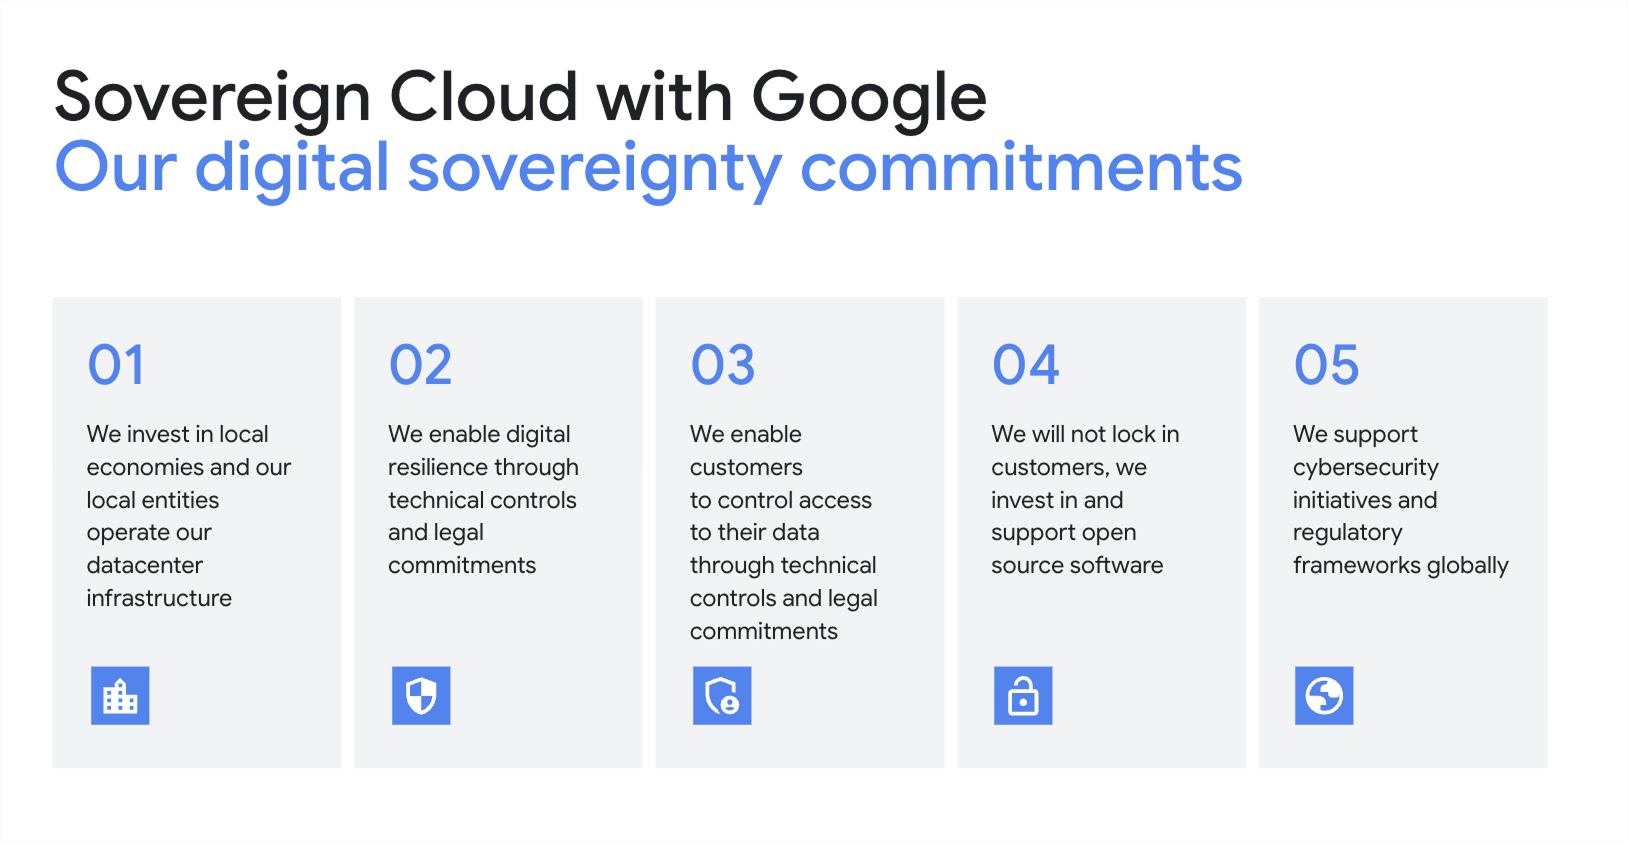
Our commitment is built on five key pillars: investing in local economies through infrastructure and workforce development; enabling digital resilience via rigorous technical and legal controls; empowering customers to control access to their unencrypted data; ensuring an open digital future by supporting open-source software and eliminating lock-in; and actively supporting global cybersecurity and regulatory frameworks.
Investing in local economies, infrastructure, and skills
True digital sovereignty begins with strong local foundations. We invest directly in regional data center infrastructure, collaborate with local technology providers, and fund comprehensive technical training programs. This approach ensures communities develop domestic engineering talent, creates sustainable jobs, and builds a self-reliant digital economy.
Assurance of operational continuity
Public sector systems, healthcare networks, and essential infrastructure require uninterrupted uptime. We provide resilient cloud deployments—including sovereign partner-operated and air-gapped environments—designed to withstand global network disruptions. Your core systems stay operational, secure, and fully aligned with local regulatory requirements.
Google Cloud Dedicated is designed to operate for up to 12 months in the unlikely scenario that its connection to Google is severed.
Google Distributed Cloud air-gapped cannot be remotely accessed or shut down by Google.
Keeping you in total control of your sensitive data
Organizations must retain absolute authority over where their information lives and who can access it. We provide tools to enforce strict data residency, manage your own encryption keys externally, and prevent unauthorized third-party access. We also removed data transfer fees entirely, ensuring you are never trapped by punitive exit costs.
Delivering modern capabilities without proprietary lock-in
National security and regulatory compliance should never force you to compromise on innovation. By building on open standards like Kubernetes and flexible architecture, we enable you to run workloads across diverse environments and deploy cutting-edge AI safely. You gain access to industry-leading tools while retaining complete technical independence.
Supporting global cybersecurity and regulatory frameworks
We collaborate with national cybersecurity agencies, financial regulators, and standards bodies worldwide to help organizations meet rigorous mandates—including ANSSI SecNumCloud 3.2 in France, BSI C5 in Germany, the EU AI Act, DORA, NIS2, Protected B in Canada, IRAP in Australia, ISMAP in Japan, MTCS Tier 3 in Singapore, as well as FedRAMP and DoD Impact Levels in the United States.
Our digital sovereignty commitments
Our commitment is built on five key pillars: investing in local economies through infrastructure and workforce development; enabling digital resilience via rigorous technical and legal controls; empowering customers to control access to their unencrypted data; ensuring an open digital future by supporting open-source software and eliminating lock-in; and actively supporting global cybersecurity and regulatory frameworks.
Investing in local economies, infrastructure, and skills
True digital sovereignty begins with strong local foundations. We invest directly in regional data center infrastructure, collaborate with local technology providers, and fund comprehensive technical training programs. This approach ensures communities develop domestic engineering talent, creates sustainable jobs, and builds a self-reliant digital economy.
Assurance of operational continuity
Public sector systems, healthcare networks, and essential infrastructure require uninterrupted uptime. We provide resilient cloud deployments—including sovereign partner-operated and air-gapped environments—designed to withstand global network disruptions. Your core systems stay operational, secure, and fully aligned with local regulatory requirements.
Google Cloud Dedicated is designed to operate for up to 12 months in the unlikely scenario that its connection to Google is severed.
Google Distributed Cloud air-gapped cannot be remotely accessed or shut down by Google.
Keeping you in total control of your sensitive data
Organizations must retain absolute authority over where their information lives and who can access it. We provide tools to enforce strict data residency, manage your own encryption keys externally, and prevent unauthorized third-party access. We also removed data transfer fees entirely, ensuring you are never trapped by punitive exit costs.
Delivering modern capabilities without proprietary lock-in
National security and regulatory compliance should never force you to compromise on innovation. By building on open standards like Kubernetes and flexible architecture, we enable you to run workloads across diverse environments and deploy cutting-edge AI safely. You gain access to industry-leading tools while retaining complete technical independence.
Supporting global cybersecurity and regulatory frameworks
We collaborate with national cybersecurity agencies, financial regulators, and standards bodies worldwide to help organizations meet rigorous mandates—including ANSSI SecNumCloud 3.2 in France, BSI C5 in Germany, the EU AI Act, DORA, NIS2, Protected B in Canada, IRAP in Australia, ISMAP in Japan, MTCS Tier 3 in Singapore, as well as FedRAMP and DoD Impact Levels in the United States.
Customers globally across jurisdictions are meeting varying sovereignty needs
Operating Partners
Operating Partners
We partner with independent national operators, telecom leaders, and global systems integrators—operating under local law—to deliver regional oversight, external key custody, and dedicated sovereign cloud operations worldwide.
Explore sovereign cloud resources
- Sovereign AI on your terms: Build and scale AI without compromising controlExplore a practical architecture across infrastructure, data, models, and agents to tune AI controls to workload risk.
Whitepaper · 12-min read
Read whitepaper - Digital sovereignty on public cloud: Google Cloud Data BoundaryLearn how governments and regulated enterprises enforce data residency, external key control, and partner oversight on public cloud.
Whitepaper · 9-min read
Read whitepaper - The Forrester Wave: Sovereign Cloud Platforms, Q2 2026Access the evaluation naming Google Cloud a Leader across sovereign cloud deployment models, data controls, and AI innovation.
Analyst report · 8-min read
Get the report
- Google Distributed Cloud powers AI at the tactical edgeSee how the U.S. Air Force deployed ruggedized Google Distributed Cloud at Mobility Guardian 2025 for disconnected AI and analytics.
Public sector blog · 6-min read
Read blog - Gemini sovereign enterprise search on Google Distributed CloudDeploy managed retrieval-augmented generation (RAG) search with source citations completely inside your air-gapped perimeter.
Hybrid cloud blog · 5-min read
Read blog - New innovations in Google Distributed CloudExplore the latest hardware, security, and sovereign AI updates across connected and air-gapped Google Distributed Cloud.
Hybrid cloud blog · 6-min read
Read blog
- Gemini is now available anywhereBring multimodal Gemini models to on-premises and air-gapped environments for regulated enterprise and national security workloads.
Hybrid cloud blog · 5-min read
Read blog - Google Distributed Cloud achieves U.S. DoD Impact Level 6 (IL6)Learn how Google Distributed Cloud air-gapped supports classified national security missions with DoD IL6 authorization.
Public sector blog · 5-min read
Read blog - Google Distributed Cloud at Next '26Discover how organizations are scaling sovereign AI and mission-critical workloads from data centers to the disconnected edge.
Hybrid cloud blog · 5-min read
Read blog
- Google Cloud named a Leader in The Forrester Wave: Sovereign Cloud PlatformsRead how our sovereignty-by-design architecture and regional partner ecosystem earned Leader recognition in the Q2 2026 report.
Security blog · 5-min read
Read blog - Choice, compliance, and collaboration: Europe's path to digital sovereigntyExamine how open cloud architectures, verifiable controls, and local European partnerships support autonomy and competitiveness.
Security blog · 6-min read
Read blog - Sovereignty and European competitiveness: A partnership-led approach to AIHow European enterprises and public institutions can capture AI-driven growth while maintaining strict local governance and control.
Security blog · 6-min read
Read blog
- Cloud CISO Perspectives: Our 2026 cybersecurity forecast reportStrategic insights from Google Cloud security leaders on board-level digital sovereignty, AI governance, and cyber resilience.
CISO perspectives · 7-min read
Read blog - Enhanced CJIS 6.0 compliance and expanded AI for public safetySee how justice and public safety agencies meet CJIS 6.0 requirements using Google Cloud Data Boundary via Assured Workloads.
Public sector blog · 5-min read
Read blog - Cloud CISO Perspectives: How digital sovereignty builds better borders for the futureWhy modern digital sovereignty requires structural controls over personnel access, inspectability, and operational survivability.
CISO perspectives · 6-min read
Read blog
Reports and compliance
- Sovereign AI on your terms: Build and scale AI without compromising controlExplore a practical architecture across infrastructure, data, models, and agents to tune AI controls to workload risk.
Whitepaper · 12-min read
Read whitepaper - Digital sovereignty on public cloud: Google Cloud Data BoundaryLearn how governments and regulated enterprises enforce data residency, external key control, and partner oversight on public cloud.
Whitepaper · 9-min read
Read whitepaper - The Forrester Wave: Sovereign Cloud Platforms, Q2 2026Access the evaluation naming Google Cloud a Leader across sovereign cloud deployment models, data controls, and AI innovation.
Analyst report · 8-min read
Get the report
Sovereign AI and edge
- Google Distributed Cloud powers AI at the tactical edgeSee how the U.S. Air Force deployed ruggedized Google Distributed Cloud at Mobility Guardian 2025 for disconnected AI and analytics.
Public sector blog · 6-min read
Read blog - Gemini sovereign enterprise search on Google Distributed CloudDeploy managed retrieval-augmented generation (RAG) search with source citations completely inside your air-gapped perimeter.
Hybrid cloud blog · 5-min read
Read blog - New innovations in Google Distributed CloudExplore the latest hardware, security, and sovereign AI updates across connected and air-gapped Google Distributed Cloud.
Hybrid cloud blog · 6-min read
Read blog
- Gemini is now available anywhereBring multimodal Gemini models to on-premises and air-gapped environments for regulated enterprise and national security workloads.
Hybrid cloud blog · 5-min read
Read blog - Google Distributed Cloud achieves U.S. DoD Impact Level 6 (IL6)Learn how Google Distributed Cloud air-gapped supports classified national security missions with DoD IL6 authorization.
Public sector blog · 5-min read
Read blog - Google Distributed Cloud at Next '26Discover how organizations are scaling sovereign AI and mission-critical workloads from data centers to the disconnected edge.
Hybrid cloud blog · 5-min read
Read blog
Strategy and policy
- Google Cloud named a Leader in The Forrester Wave: Sovereign Cloud PlatformsRead how our sovereignty-by-design architecture and regional partner ecosystem earned Leader recognition in the Q2 2026 report.
Security blog · 5-min read
Read blog - Choice, compliance, and collaboration: Europe's path to digital sovereigntyExamine how open cloud architectures, verifiable controls, and local European partnerships support autonomy and competitiveness.
Security blog · 6-min read
Read blog - Sovereignty and European competitiveness: A partnership-led approach to AIHow European enterprises and public institutions can capture AI-driven growth while maintaining strict local governance and control.
Security blog · 6-min read
Read blog
- Cloud CISO Perspectives: Our 2026 cybersecurity forecast reportStrategic insights from Google Cloud security leaders on board-level digital sovereignty, AI governance, and cyber resilience.
CISO perspectives · 7-min read
Read blog - Enhanced CJIS 6.0 compliance and expanded AI for public safetySee how justice and public safety agencies meet CJIS 6.0 requirements using Google Cloud Data Boundary via Assured Workloads.
Public sector blog · 5-min read
Read blog - Cloud CISO Perspectives: How digital sovereignty builds better borders for the futureWhy modern digital sovereignty requires structural controls over personnel access, inspectability, and operational survivability.
CISO perspectives · 6-min read
Read blog

Compliance regimes and data boundaries by country
Fulfill local data residency and cross-jurisdictional sovereignty requirements on your terms. Google Cloud offers regional data boundaries on public cloud, partner-operated local clouds, and fully air-gapped infrastructure. Explore over 180 global standards in our Compliance Resource Center.
AI trust and transparency
Accelerate your AI initiatives securely with Google Cloud. We combine advanced safety research with robust data governance and compliance controls. Explore our AI Trust and Transparency Resource Center.