Maintains 100% gateway uptime during orbital passes using Google Kubernetes Engine (GKE)
Secures space-to-ground data translation using Confidential VMs
Validates physical host provenance with Google Cloud PPID capabilities
Slashes bespoke satellite infrastructure integration from weeks to a weekend
SpaceComputer leverages Google Cloud Confidential VMs and GKE to deliver verifiable, zero-downtime space-to-ground data gateways.
SpaceComputer leverages Google Cloud Confidential VMs and GKE to deliver verifiable, zero-downtime space-to-ground data gateways.
Overcoming the ‘black box’ trust barrier in space-to-ground communications
SpaceComputer is an open infrastructure layer connecting the global space economy. Its core platform, Orbitport, acts as a universal gateway between terrestrial applications on Earth and in-space infrastructure.
Historically, communicating with satellites required navigating fragmented, proprietary ground-station interfaces. Furthermore, translating terrestrial data protocols (like TLS) into space protocols (like CSP) created a massive security vulnerability. Because protocol translation requires exposing data in memory at the gateway, an operator proxy becomes a highly privileged component. With compromised commands risking the permanent de-orbiting of multi-million-dollar satellites, operators were extremely hesitant to trust third-party proxies. SpaceComputer set out to eliminate blind trust entirely, replacing organizational assurances with mathematical, independent verifiability.
Google Cloud lets a lean team consume mature infrastructure—Confidential VMs, GKE, IAM, and KMS—rather than rebuilding it. That gives us immense leverage to focus on space security architecture rather than managing underlying servers.
Filip Rezabek
Co-founder and CTO, SpaceComputer
To achieve this, SpaceComputer evaluated hyperscale confidential computing environments. Google Cloud emerged as the clear choice because its Intel TDX implementation offered the closest experience to native, bare-metal deployments while operating at cloud scale. Crucially, Google Cloud offered Platform Provider ID (PPID) host provenance capabilities. This lets SpaceComputer’s clients run remote hardware attestation checks, mathematically proving not only that Orbitport runs on genuine Intel TDX hardware, but also that the physical host server is authentically part of Google Cloud. Supported by the Google Cloud Startup Program, SpaceComputer utilized Google Cloud to rapidly deploy an enterprise-grade, space-certifiable security layer.
Delivering 100% uptime during 15-minute orbital passes with GKE
Spacecraft communication windows last just 15 to 20 minutes as satellites pass overhead. During that brief window, Orbitport has to establish ground connections, authenticate services, route commands, and translate protocols flawlessly. If a gateway fails, the next transmission window may be hours away.
Google Cloud Intel TDX implementation is as close as possible to native deployments. Features like host provenance prove Orbitport runs on genuine TDX hardware inside Google Cloud, giving our clients complete confidence in our verifiable infrastructure.
Filip Rezabek
Co-founder and CTO, SpaceComputer
SpaceComputer orchestrates its platform using Google Kubernetes Engine (GKE) to manage hardened Confidential VMs. Before clients transmit sensitive data, they execute hardware attestation checks against Orbitport to verify software measurements. Once verified, GKE handles high-throughput capacity scaling without adding cryptographic overhead to every byte. Managed GKE and Identity and Access Management (IAM) controls have eliminated manual infrastructure debugging for SpaceComputer’s lean engineering team, maintaining 100% Orbitport uptime during operational passes while transferring gigabytes of data. Abstracting satellite integration into simple APIs has also transformed developer speed, slashing bespoke integration timelines from weeks down to a single weekend.
To future-proof the platform, SpaceComputer is rolling out post-quantum cryptography (TLS with ML-KEM) to protect against ‘harvest now, decrypt later’ threats.
SpaceComputer is also building modular key management options, allowing enterprise clients to choose between self-managed keys or native Cloud Key Management Service (KMS) integration. Looking ahead, SpaceComputer plans to explore Gemini for automated telemetry analysis and anomaly detection, establishing an interconnected ‘Space Fabric’ spanning Earth and orbit.
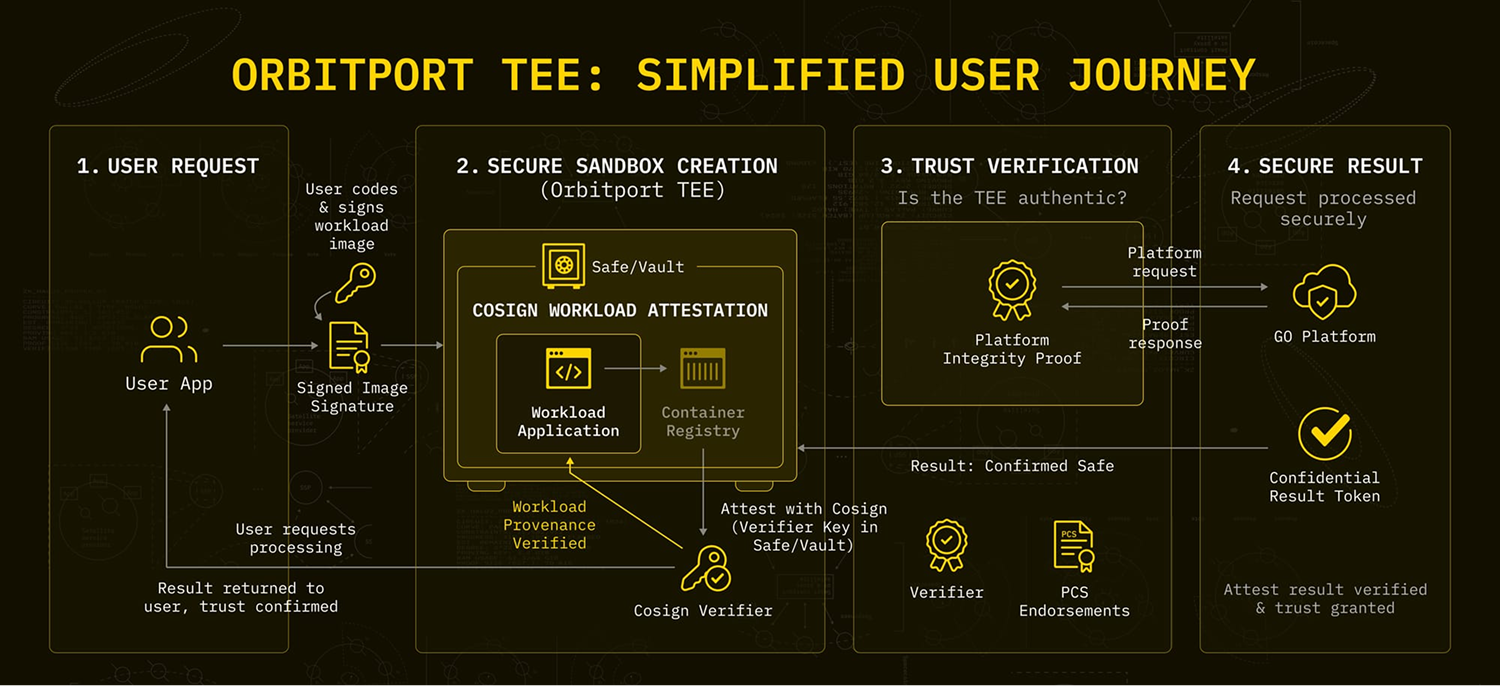
SpaceComputer is an open infrastructure layer connecting the space economy. Its Orbitport platform provides a secure, independently verifiable gateway for seamless communication between terrestrial applications and orbital infrastructure.
Industry: Technology
Location: Singapore
Products: Confidential Computing, Google Kubernetes Engine (GKE), Identity and Access Management (IAM), Google Cloud Command Line Interface (gcloud CLI), Cloud Key Management Service (KMS), Gemini